What Is a SOC 1 Report? Type 1 vs. Type 2 Explained
In order to pass your lease accounting audit under ASC 842. IFRS 16 or GASB, your external auditors will likely ask for your SOC 1 report. So what is a SOC 1 compliance report, and why is it important? In short, a SOC 1 Report is an audit report that
A SOC 1 report is an independent auditor's examination of a service organization's controls that are relevant to its customers' financial reporting. It helps businesses and their auditors understand whether a third-party provider has appropriate controls in place to support financial information.
For companies relying on external accounting software, this can be an important part of the audit process. When a business uses lease accounting software to calculate liabilities, maintain financial schedules, or prepare journal entries, the reliability of the information matters.
However, not all SOC reports provide the same assurance. Understanding the differences between SOC 1 Type 1, SOC 1 Type 2, and SOC 2 helps finance teams evaluate vendors and determine which reports are relevant to their financial reporting requirements.
What Is a SOC 1 Report?
SOC 1 stands for System and Organization Controls 1. A SOC 1 report examines controls at a service organization that are relevant to a customer's internal control over financial reporting (ICFR). These examinations are performed by independent CPA firms under the applicable attestation standards established by the American Institute of Certified Public Accountants (AICPA).
Service organizations include businesses that perform outsourced processes for other companies, such as payroll providers, financial transaction processors, and certain accounting software vendors.
For example, a company using third-party software to process financial information may rely on controls operated by the provider. A SOC 1 report helps the company's auditors understand those controls and assess whether they can be considered when planning the financial statement audit.
It's important to understand that SOC 1 is not a general security certification or a guarantee of accurate financial statements. The report addresses specified controls within a defined system and reporting scope.
SOC 1 Type 1 vs. Type 2: What's the Difference?
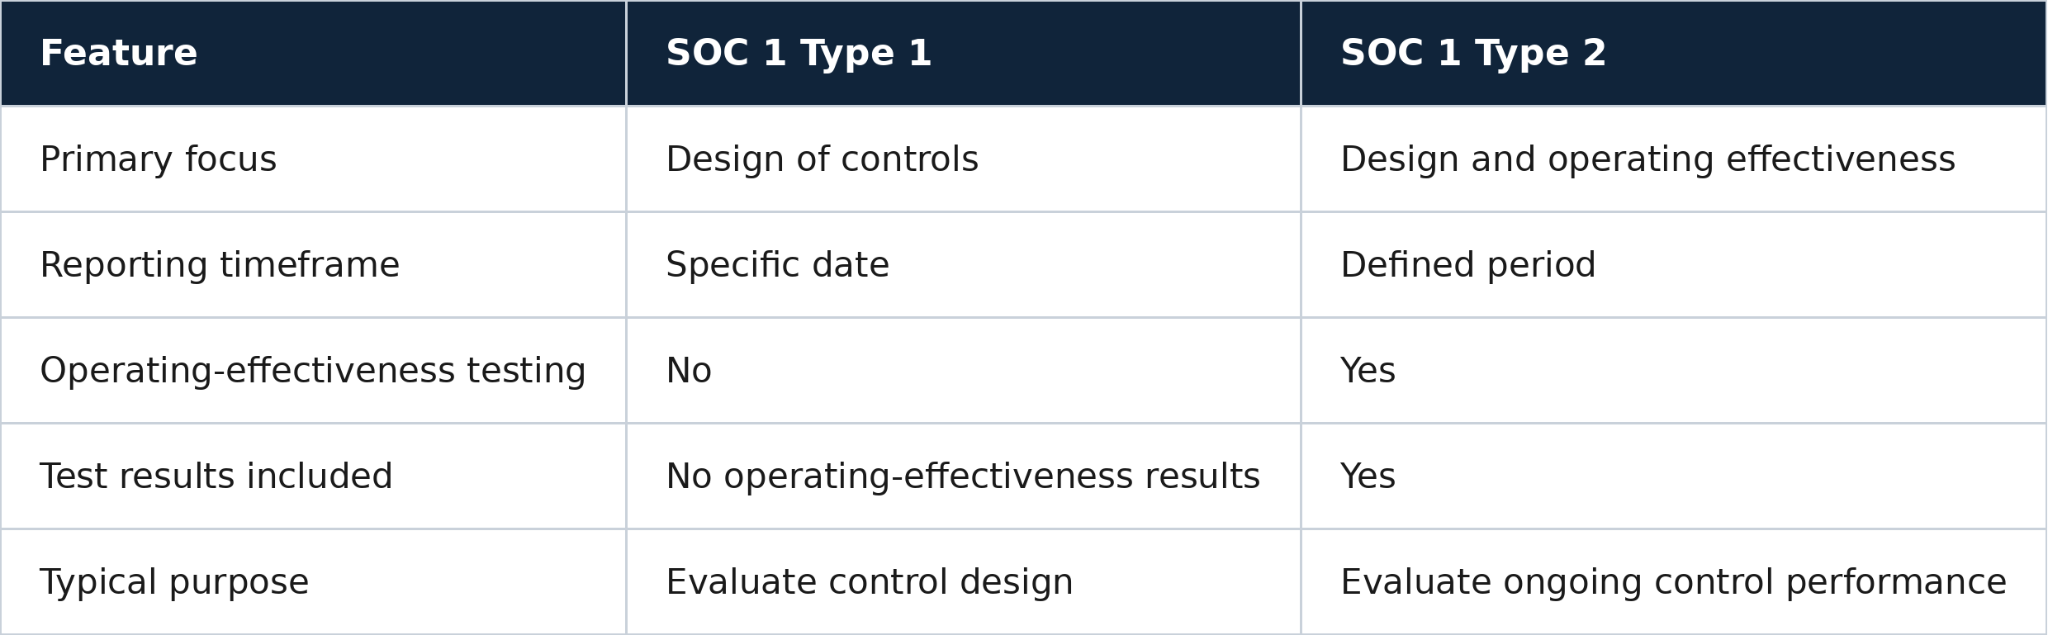
There are two types of SOC 1 reports. Both evaluate controls relevant to financial reporting, but the difference lies in what the auditor examines and the period covered.
SOC 1 Type 1 Report
A SOC 1 Type 1 report evaluates whether a service organization's system description is fairly presented and whether its controls are suitably designed to achieve the stated control objectives as of a specific date.
For instance, a software vendor may have procedures for approving system changes, managing user access, and protecting financial records. A Type 1 examination evaluates whether the relevant controls are appropriately designed at the reporting date.
However, it does not provide an opinion on whether those controls operated effectively over an extended period.
SOC 1 Type 2 Report
A SOC 1 Type 2 report goes further by examining both the design and operating effectiveness of controls over a specified period, commonly six or twelve months.
The auditor tests whether relevant procedures operated as intended and documents the results, including any exceptions identified during testing.
For a lease accounting software provider, this may include examining how changes to financial processing systems were approved and whether relevant controls operated throughout the reporting period.
Because Type 2 reports include operating-effectiveness testing, they often provide more useful evidence for financial statement audits involving ongoing outsourced processes.
Neither type guarantees that every transaction is accurate. Finance teams must still consider the report's scope, any exceptions, and their own internal control responsibilities.
SOC 1 vs. SOC 2: Key Differences
Although SOC 1 and SOC 2 are both independent assurance reports, they serve different purposes.
SOC 1 focuses on financial reporting controls. It is intended to help customers and their financial statement auditors assess controls at service organizations that may affect financial reporting.
SOC 2 focuses on controls evaluated against the AICPA's Trust Services Criteria. These criteria address security, availability, processing integrity, confidentiality, and privacy, with the applicable categories depending on the engagement.
For example, a cloud-based software provider may obtain a SOC 2 report to demonstrate that relevant controls have been evaluated against its security and other selected trust services commitments. If the provider's services also affect customers' financial reporting, a SOC 1 examination may be relevant.
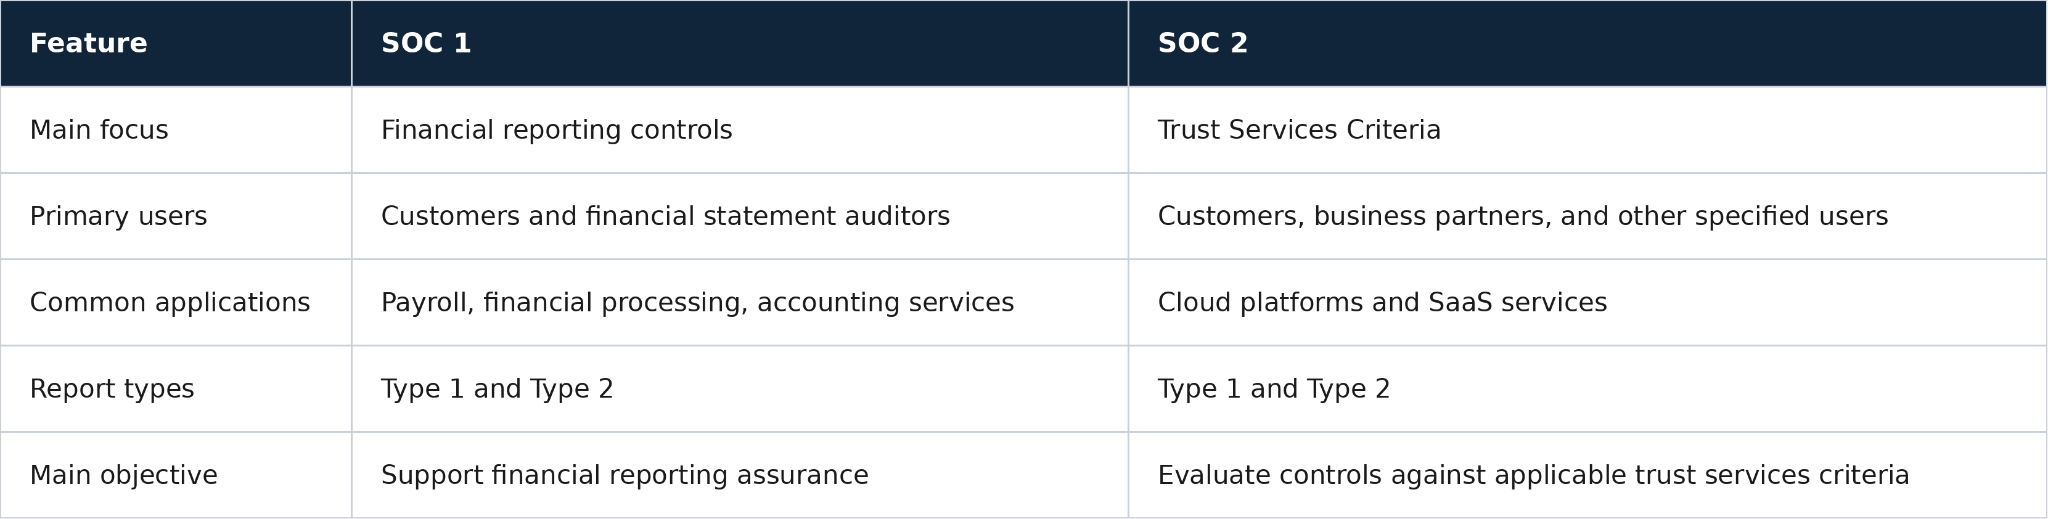
One report does not automatically replace the other. A SOC 2 report may address important security risks without providing the specific assurance over financial reporting controls that a customer or auditor needs.
What Does a SOC 1 Report Include?
A SOC 1 report contains information about the service organization's system, relevant controls, and the independent auditor's findings.
It generally includes management's description of the system and assertion, the service auditor's opinion, and details of the control objectives and related controls.
A Type 2 report also includes descriptions of the auditor's operating-effectiveness tests and the results of those tests.
The auditor's opinion is particularly important. It explains the conclusions reached within the engagement's scope and identifies whether the opinion has been modified.
Finance teams should also review any testing exceptions. An exception doesn't automatically mean the provider's entire control environment is ineffective, but it may require further investigation depending on the affected control.
Why Do SOC 1 Reports Matter for Lease Accounting Software Vendors?
Commercial lease accounting involves financial information that directly affects an organization's financial statements.
Under ASC 842, lessees generally recognize lease liabilities and right-of-use assets for applicable leases. These amounts depend on accurate lease terms, payment schedules, discount rates, and other accounting assumptions.
Consider a retailer managing 100 commercial leases. Its finance team relies on software to calculate lease liabilities, maintain schedules, and prepare journal entries.
If the software processes information incorrectly or relevant system changes are not appropriately controlled, the resulting financial information could contain errors.
A SOC 1 report may provide evidence about the provider's relevant financial processing controls, including change management, access controls, and other activities included within the examination's scope.
However, the customer remains responsible for its own accounting decisions, source data, and financial statement reporting.
Supporting Financial Statement Audits
During an audit, external auditors may need to understand the controls surrounding third-party systems used to process financial information.
A relevant SOC 1 Type 2 report can provide evidence about controls operating at the software provider, potentially reducing the need for certain additional procedures at the service organization.
Auditors must still assess whether the report covers the systems and processes used by their client.
They may also review lease agreements, recalculate selected balances, examine journal entries, and test the customer's internal procedures.
These responsibilities are part of broader lease audit procedures and cannot be replaced simply by obtaining a vendor's SOC 1 report.
How to Review a SOC 1 Report From a Software Vendor
Receiving a SOC 1 report is only the first step. Finance teams should evaluate whether it provides meaningful evidence for the services they use.
Several areas deserve particular attention.
Review the Scope and Reporting Period
Confirm that the report covers the relevant software, services, and financial processing activities.
A report covering one product or business unit may not address another product offered by the same vendor.
The reporting period also matters. If the report ends before the customer's financial year-end, auditors may request additional information about the period not covered.
Examine the Auditor's Opinion and Exceptions
Read the independent auditor's opinion and determine whether it contains any qualifications or other modifications.
For Type 2 reports, review the control testing results and identified exceptions.
An exception affecting a financial processing control may be more relevant to a lease accounting audit than one involving an activity unrelated to the customer's financial reporting.
Identify Customer Responsibilities
SOC 1 reports may include complementary user entity controls (CUECs). These are controls that customers are expected to perform as part of the overall control environment.
For lease accounting, they may involve approving lease changes, validating contract information, reviewing system access, and reconciling financial reports.
Documenting these responsibilities is an important part of establishing reliable lease accounting policies and controls.
Organizations should also review any relevant subservice organization exclusions and discuss additional assurance needs with their auditors.
Is a SOC 1 Report Required for Lease Accounting Software?
Not every lease accounting software vendor is required to obtain a SOC 1 report.
ASC 842 establishes lease accounting requirements, but it does not impose a blanket SOC 1 reporting requirement on software providers.
Whether a SOC 1 report is necessary depends on how the service affects the customer's financial reporting, the relevant risks, and the evidence required by the customer's auditors.
For example, a company using software mainly to organize lease documents may have different assurance requirements from one relying heavily on a provider's financial processing controls.
If a vendor does not have a SOC 1 report, finance teams should discuss whether alternative evidence or additional procedures can address the relevant risks.
The goal is to obtain appropriate assurance, not simply to collect a report.
Evaluating Lease Accounting Software and Financial Controls
SOC reports are useful when assessing software vendors, but they should be considered alongside the platform's accounting capabilities and operational processes.
Finance teams should understand how software handles lease calculations, modifications, journal entries, reporting, and user permissions.
They should also evaluate how financial information moves between real estate and accounting teams. An overlooked lease amendment or incorrect payment schedule can create problems even when the software provider maintains appropriate controls.
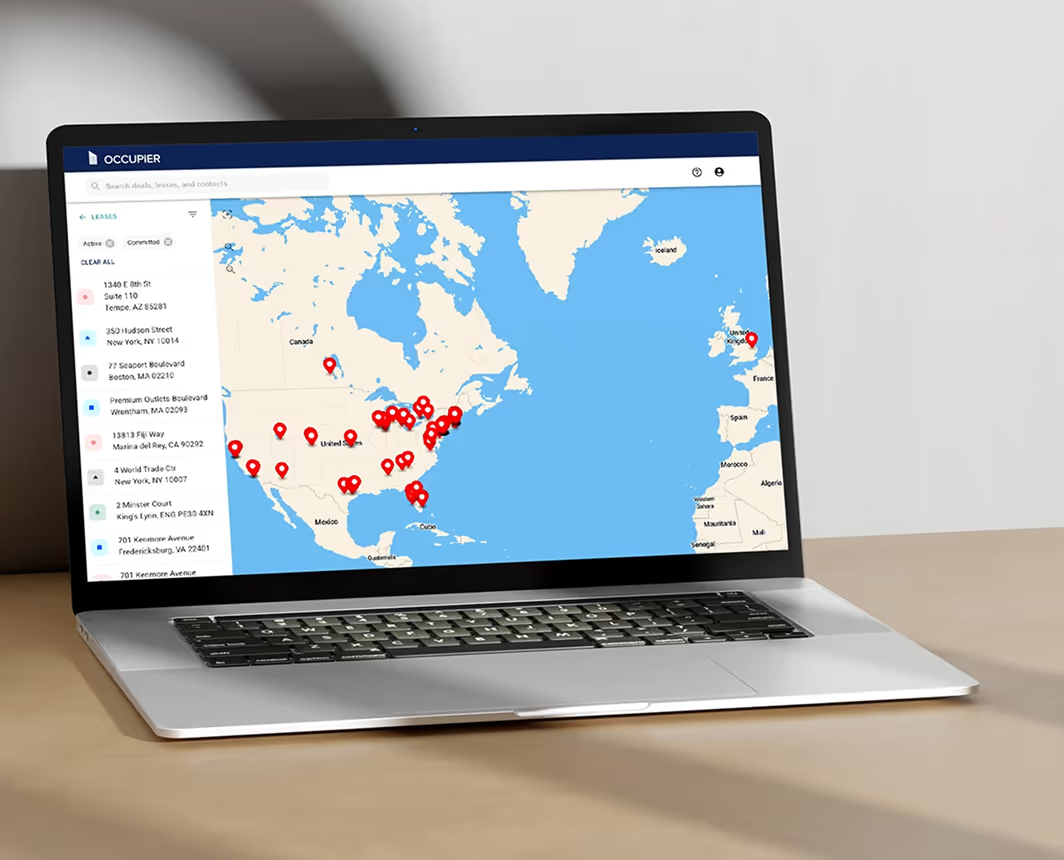
Occupier's lease accounting software connects lease information with accounting schedules, journal entries, and reporting. This helps real estate and finance teams maintain consistent records as leases change.
Regardless of the platform selected, businesses should evaluate relevant vendor assurance documentation while maintaining their own review and reconciliation procedures.
A structured lease accounting audit checklist can help finance teams organize supporting documentation before an audit.
Frequently Asked Questions About SOC 1 Reports
What Does SOC 1 Stand For?
SOC 1 stands for System and Organization Controls 1. It refers to an independent examination report covering service organization controls relevant to customers' internal control over financial reporting.
Is SOC 1 Type 2 Better Than Type 1?
A Type 2 report provides additional assurance about operating effectiveness because it covers controls over a specified period. However, the appropriate report depends on the risks, services, and audit requirements being evaluated.
Is a SOC 1 Report the Same as a SOC 2 Report?
No. SOC 1 addresses controls relevant to financial reporting, while SOC 2 addresses controls evaluated against applicable Trust Services Criteria. A provider may obtain one or both depending on its services and customer requirements.
Does ASC 842 Require a SOC 1 Report?
No. ASC 842 does not automatically require lease accounting software vendors to maintain a SOC 1 report. However, customers and auditors may request relevant assurance when third-party services affect financial reporting.
How Often Should a SOC 1 Report Be Reviewed?
Organizations commonly review relevant SOC 1 reports as part of annual audit preparation and vendor oversight. The appropriate frequency depends on the services being used, the risks involved, and the organization's control requirements.
Lease management that works for real estate and finance
15,000 sq ft
90 days notice
March 2026
Action required